
Maksym Stepanenko
Managing Partner, Crystal Tax
International client projects since 2012: company structures, tax, immigration, DUNS and NCAGE. 50+ jurisdictions.
A GDPR privacy policy for your website, SaaS or app, plus a cookie policy, terms of service, a public offer under Ukrainian law and a DPA, written around how your product actually processes data.
Since 2012 · 50+ jurisdictions · GDPR, Ukraine, US · documents in English, Ukrainian, Russian and other languages
In brief
Pick the situation closest to yours: a short outline of the route and the first step.
We determine where you are the controller and where you process client data as a processor, and write the Privacy Policy, Terms of Service, a DPA for B2B clients and a public subprocessor list. We also check whether you need an EU representative under Article 27.
Example. A booking service for beauty salons received a set of policy, terms of use and DPA before launching in Poland; its first corporate client signed the DPA after one round of edits.
Discuss this case →We check which data the app and its SDKs collect, align the policy and the App Privacy and Data safety answers, and place the policy link in the app and in the developer console.
Example. A fitness app was rejected because its policy omitted an analytics SDK that collected the device identifier. After the review and new questionnaire answers, the build was accepted.
Discuss this case →We prepare a public offer under Ukrainian law with a clear acceptance procedure at checkout, a privacy policy under the Ukrainian personal data protection law, and delivery and returns rules.
Example. A home goods store replaced a public offer copied from another website with a text built around its own payment, delivery and returns, and disputed customer requests started to be handled under clear rules.
Discuss this case →We compile the record of processing, align the policies with how the product really works, put DPAs in place with contractors and prepare answers to the review questions. In parallel we look at the corporate documents.
Example. A B2B procurement marketplace, three weeks before due diligence, received a record of processing, an updated policy and signed DPAs with its hosting and CRM providers.
Discuss this case →We inventory cookies and trackers, split them into strictly necessary and consent-based, write the Cookie Policy and banner texts, and give the developer the logic: optional scripts stay off until consent.
Example. An online school using pixels from two ad networks got a banner with “Accept” and “Reject” buttons on the first screen and settings by category.
Discuss this case →We check the client's DPA against how you really work: instructions, subprocessors, incident notification deadlines, audits, transfers outside the EU, liability. We prepare redlines and a negotiating position.
Example. An HR platform developer agreed with a European client on a reasonable incident notification deadline and on audits based on reports instead of on-site inspections.
Discuss this case →A turnkey GDPR privacy policy starts with a data map of your product: we write the documents once we understand which data you collect, from whom, why, on what legal basis, where you store it and which services you pass it to. Crystal Tax lawyers carry the work from the questionnaire to final texts in the languages you need.

Generators and templates produce a text that describes someone else's product. Regulators, app stores and the lawyers of B2B clients check exactly the gap between the policy and real processing: the text omits analytics running on the site, states a retention period nobody follows, or leaves out the payment provider.
We check each of these points against the data map before handing the texts over for publication.
| Situation | Documents |
|---|---|
| Website with forms and analytics, users in the EU | GDPR privacy policy, Cookie Policy and consent banner, DPAs with contractors |
| SaaS for business clients in the EU and the UK | Terms of Service, Privacy Policy, DPA for clients, subprocessor list, record of processing |
| Mobile app | Privacy policy for the app linked in the console and inside the app, App Privacy and Data safety answers, user terms |
| Online store in Ukraine | Public offer under Ukrainian law, privacy policy under Ukrainian law, delivery and returns rules |
| Users in the US | Privacy Policy reflecting state requirements; for California, a check of whether CCPA and CPRA apply |
We prepare documents in Russian, Ukrainian and English; other languages go through vetted translators, and we proofread the terminology. When the product changes, for example a new payment provider or market appears, we update the data map and the texts as a one-off job or as part of ongoing legal support for startups, which also covers GDPR compliance for startups.
Usually, in our experience, the document package for one product is ready within 1–3 weeks after the data questionnaire is completed. The timeline depends on the case, its details, the work of the authorities and force majeure.
The review period for an app in App Store or Google Play is set by the platform itself; we influence only the quality of the answers and how closely the policy matches the real app.
The work takes longer when the developer is external and slow to respond, when the product uses many SDKs with unclear data transfers, when there is health data, children's data or biometrics, or when a B2B client sends its own DPA with strict terms. We name these points at the start.
The cost of a GDPR privacy policy and a document package, including the work a terms and conditions lawyer would do on your Terms of Service, is calculated individually: it depends on how much data and how many services the product uses and which markets it enters.
Describe the product in a few sentences, and we will assess the work within one working day. A first answer and a detailed review are available at a consultation: 30 minutes online — 100 euros; a written opinion starts from 200 euros.
Five reasons founders trust us with their privacy policy, public offer and data contracts.
Company, contracts, data documents, bank account, accounting and taxes, including Ukrainian CFC (controlled foreign company) rules and the CFC report, with no need to look for separate contractors. You make the decisions and sign; we do the rest.
Answering App Store and Google Play remarks, corresponding with the client's lawyers on a DPA and handling bank questions is our job. We handle refusals, queries and stalled deadlines at no extra charge until the matter is closed.
Your case won’t get lost along the way: we carry it to the result, even if the process takes months. We remain answerable to you for the result.
An experienced specialist handles your case personally, backed by Crystal Tax’s 14 years of practice in 50+ countries. We know the requirements of registrars, banks, tax offices and the lawyers of large clients from our own cases.
Information about you, your company and your deals does not reach competitors or third parties. We disclose only what the law or a procedure requires, and this is set out in the contract.
The work runs in six steps, and at each one you know what we need from you.
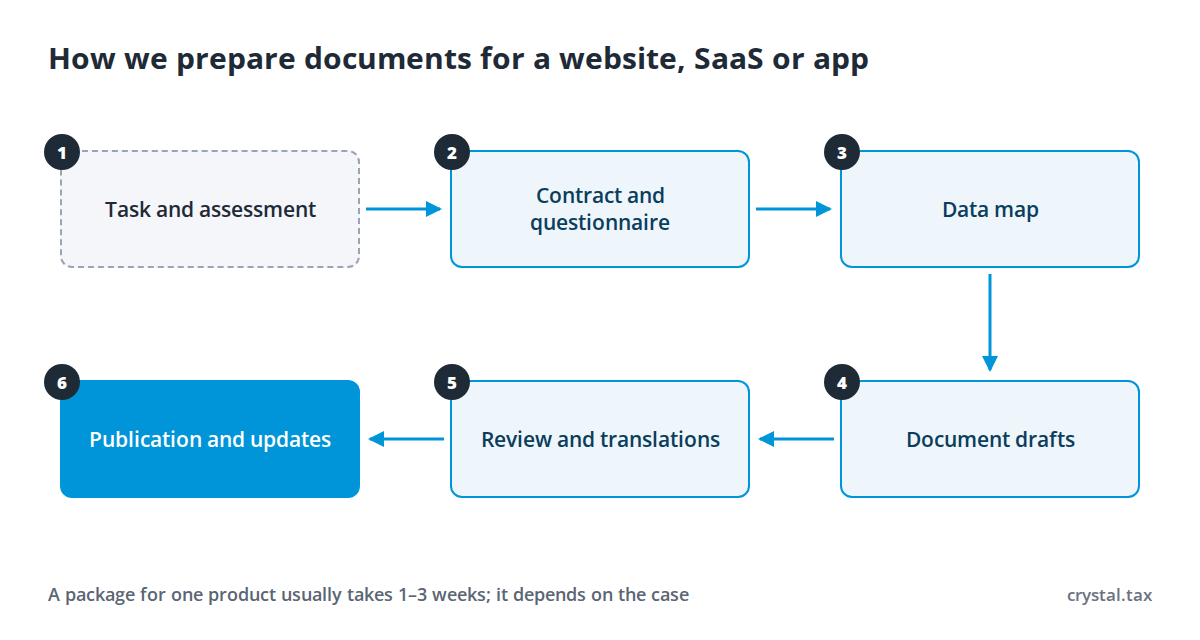
To start, we need information about the company, the product and the services it uses; we provide the questionnaire and the list of questions.
If other lawyers have already prepared documents for you, send them over: we will check what can stay and what diverges from the product or from other documents in the package.
Article 13 GDPR lists the information a controller provides when collecting data from the user directly, and Article 14 covers data obtained from other sources.
Under Article 14, the categories of data and their source are also stated. The information is provided within a reasonable period, at the latest within one month of obtaining the data, and, if the data is used to communicate with the user or disclosed to another recipient, at the latest at the first communication or first disclosure.
The maximum fine for infringing data subjects' rights and the basic principles under Article 83(5) GDPR is up to 20,000,000 euros or, for an undertaking, up to 4 percent of total worldwide annual turnover of the preceding financial year, whichever is higher.
Each of the five documents has its own job, and in practice they refer to each other, so they are written together.
| Document | Purpose | Who needs it | Legal basis |
|---|---|---|---|
| Privacy Policy | Tell users how their data is processed | Any website or app that collects personal data | GDPR, Articles 13 and 14; Law of Ukraine on personal data protection, Article 12; CCPA for California; App Store and Google Play rules |
| Cookie Policy and banner | Describe cookies and trackers and obtain consent for optional ones | Websites and services with analytics, advertising, third-party chats | ePrivacy Directive 2002/58/EC, Article 5(3); GDPR consent standard, Articles 4(11) and 7 |
| Terms of Service, user terms | Terms of use of the service, payment, liability, disputes | SaaS, platforms, apps | Contract law of the country chosen in the terms, and consumer protection |
| Public offer (Ukrainian law) | An offer to conclude a contract with anyone who accepts the terms | Online stores and services selling in Ukraine | Civil Code of Ukraine, Articles 633, 641, 642; Law on e-commerce, Article 11 |
| DPA | Terms of processing data on behalf of the controller | B2B SaaS and anyone who passes data to contractors | GDPR, Article 28(3) |
A DPA under Article 28(3) must set out the subject matter, duration, nature and purpose of processing, the types of data and categories of data subjects, as well as the processor's obligations: act only on documented instructions, ensure staff confidentiality, take security measures under Article 32, engage subprocessors only with the controller's authorisation, assist with data subject requests and with the obligations under Articles 32–36, delete or return the data after the end of the services, make information available and allow audits.
Under the ePrivacy Directive, consent to cookies is required for storing and reading information on the user's device. The exception is technical storage for transmitting a communication or storage strictly necessary for a service the user has explicitly requested. Under Recital 32 GDPR, silence, pre-ticked boxes and inactivity do not constitute consent.
Since 2021, following amendments by Law 1667-IX, the Civil Code of Ukraine expressly recognises as an offer documents publicly available on the internet that contain the essential terms of a contract and a proposal to conclude it with anyone who applies, regardless of whether an electronic signature is present.
For a privacy policy in Ukraine, the Law on personal data protection 2297-VI applies: Article 11 lists the grounds for processing, including consent, contract and legitimate interest, and Article 12 requires informing the data subject at the time of collection about the data owner, the data collected, their rights, the purpose of collection and the recipients.
The new consumer protection law 3153-IX was adopted in 2023 and enters into force one year after publication, but not earlier than the day martial law is terminated or lifted. As of 27.09.2026 the official portal shows its status as “entering into force”, so the current consumer protection rules apply to public offers.
Describe the product in a few sentences: what it is, which markets it enters and which services it uses. We will reply within one working day, and at a 30-minute consultation (€100) we will name the first step right away.
Regulation (EU) 2016/679 (GDPR), Articles 3, 4, 7, 13, 14, 27, 28, 30, 46, 83, Recital 32; Directive 2002/58/EC (ePrivacy) as amended by 2009/136/EC, Article 5(3); Law of Ukraine on Personal Data Protection No. 2297-VI, Articles 11 and 12; Civil Code of Ukraine, Articles 633, 641 as amended by Law 1667-IX, 642; Law of Ukraine on E-Commerce No. 675-VIII, Article 11; Law of Ukraine on Consumer Protection No. 3153-IX, final provisions; Apple, App Review Guidelines, 5.1.1 (i) Privacy Policies; Google Play, User Data policy and Data safety section; California Attorney General, California Consumer Privacy Act; California Privacy Protection Agency, CPI adjustment of CCPA thresholds from 1 January 2025. Checked: 27.09.2026.
Maksym Stepanenko
Managing Partner, Crystal Tax
International client projects since 2012: company structures, tax, immigration, DUNS and NCAGE. 50+ jurisdictions.
“Crystal Tax provided invaluable assistance in setting up our company in the United Arab Emirates…”
Yevelina K.2 years ago · Google Maps
“Opening a bank account abroad sounded scary at first, but Crystal Tax made it super easy. They knew exactly which banks to approach, what paperwork was needed…”
Sergei M.a year ago · Google Maps
“As a fast-growing startup, we needed clear, actionable tax advice — and Crystal Tax delivered exactly that. No jargon, no fluff.”
Inna M.a year ago · Google Maps
Briefly describe your task: the country, the business activity and the timing. That is enough for us to propose a solution and the order of work.
We reply within one business day.
Or message us
 Telegram
 WhatsApp